Access Control in Cyber Security: Common Challenges and Solutions
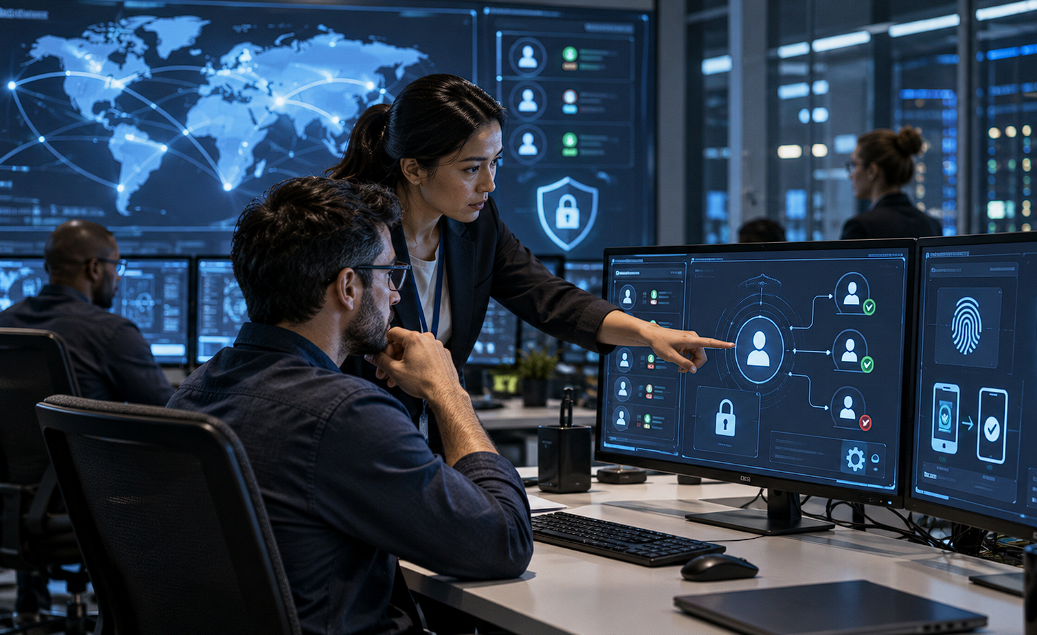
Access control is a fundamental foundation of cybersecurity. It determines who can access a system, application, network, facility, or specific resource, and what they can do once access is granted. As organizations manage more cloud services, remote workers, connected devices, and sensitive information, controlling access has become more complicated.
A strong access control strategy is not simply about creating usernames and passwords. It involves authentication, authorization, permissions, policies, monitoring, and regular reviews. NIST describes access control as the process of granting or denying requests to use information, information processing services, or enter protected facilities.
Organizations can also use different models, such as role-based or attribute-based access control, depending on their operational requirements. Understanding these approaches is important because poorly configured permissions can create unnecessary exposure even when other security measures are working properly.
1. Managing Too Many User Permissions
One of the most common access control challenges is excessive user access. Employees may receive permissions when they join a company, change departments, take on temporary responsibilities, or work on special projects. Over time, some of those permissions may no longer be necessary.
This creates a gap between what someone needs to perform their current role and what they can actually access.
The principle of least privilege provides a practical way to address this problem. Users should generally receive only the permissions required to perform their assigned responsibilities.
For organizations reviewing access control in cyber security, this principle is particularly important because access decisions need to be considered across both digital and physical environments.
Regular access reviews can identify inactive accounts, unnecessary privileges, shared credentials, and outdated permissions. Managers and system owners should review access whenever an employee changes roles or leaves the organization.
2. Dealing With Complex Access Control Policies
As organizations grow, their access policies often become more complicated. Different departments may require different permissions, while contractors, temporary workers, partners, and administrators may need separate levels of access.
A simple permission structure may work for a small team but become difficult to maintain across a larger environment.
Use Clear Access Models
Role-Based Access Control, or RBAC, assigns permissions according to a person's organizational role. For example, members of an accounting team may receive access to financial systems without receiving permissions for engineering resources.
Attribute-Based Access Control, or ABAC, can make decisions using additional attributes such as department, location, device, time, or resource sensitivity. NIST notes that ABAC can evaluate attributes associated with the user, requested resource, operation, and environmental conditions.
Organizations should select an approach that matches their operational complexity rather than creating unnecessary layers of rules.
3. Supporting Remote and Hybrid Work
Remote work has changed how organizations approach access control. Employees may connect from home networks, shared workspaces, personal devices, or different geographic locations.
A security policy that assumes users are always connecting from a trusted office network may no longer be appropriate.
Strengthen Identity Verification
Organizations can use multi-factor authentication to add another verification step beyond a password. Access decisions can also consider device status, location, user role, and the sensitivity of the requested resource.
This approach reduces reliance on a single credential and allows organizations to apply different controls based on the circumstances surrounding an access request.
4. Controlling Privileged Accounts
Administrative accounts require particular attention because they can often change configurations, create accounts, modify permissions, or access sensitive systems.
A compromised standard account may have limited impact, while a compromised privileged account can provide much broader access.
Separate Administrative Access
Organizations should avoid using administrative accounts for routine activities whenever practical. Separate accounts can be used for administrative tasks, while standard accounts handle everyday work.
Privileged access should also be logged and reviewed. Organizations can establish additional authentication requirements for sensitive actions and regularly verify which users still require elevated permissions.
5. Managing Physical and Digital Access Together
Cybersecurity discussions often focus on digital systems, but physical access can also affect information security.
Unauthorized physical access to offices, server rooms, network equipment, or other restricted areas may allow someone to interact with systems or devices directly.
Connect Physical Security With Cybersecurity
Access badges, credentials, entry systems, cameras, and other physical controls can form part of a broader security strategy. When employees leave an organization, physical credentials should be revoked along with digital accounts.
Likewise, temporary workers and visitors should receive access appropriate to their role and the duration of their visit.
Treating physical and logical access as completely separate processes can create gaps. Coordinating the two can make it easier to identify inconsistencies and revoke access promptly.
6. Handling Employee Onboarding and Offboarding
Access control can fail when account provisioning and deprovisioning are handled manually or inconsistently.
During onboarding, new employees may need access to several applications, systems, facilities, and shared resources. When someone leaves, those permissions must be removed quickly.
Create a Standardized Process
Organizations can establish an access checklist covering:
- User account creation
- Application permissions
- Group memberships
- Physical credentials
- Privileged access
- Remote access
- Shared accounts
- Device access
- Account termination
Automation can reduce repetitive administrative work, but automated processes should still be reviewed regularly to ensure permissions are being assigned correctly.
7. Monitoring Access Attempts
Access control is not complete simply because permissions have been configured. Organizations also need to understand how those permissions are being used.
Repeated failed login attempts, unusual access times, unexpected privilege changes, or attempts to access restricted resources may indicate a security issue.
Maintain Useful Audit Logs
Logs should capture relevant access activity and be retained according to organizational and regulatory requirements. Security teams can use these records to investigate incidents and identify patterns that may otherwise be difficult to notice.
Monitoring is especially valuable when access policies are complex because it provides evidence of how controls are functioning in practice.
8. Addressing Outdated or Inconsistent Policies
An access control policy can become outdated as an organization changes.
New applications may be introduced, departments may be reorganized, employees may change responsibilities, and business processes may move to cloud platforms. If access policies remain unchanged, they may no longer reflect how the organization operates.
Review Policies Regularly
Access policies should be reviewed when major organizational or technology changes occur. Security teams can also schedule periodic reviews to identify rules that are no longer necessary.
A policy should therefore be checked not only for what it says, but also for whether the implemented controls enforce it correctly.
9. Balancing Security With Usability
Overly restrictive access controls can create operational problems. If employees repeatedly encounter unnecessary access barriers, they may look for workarounds or request broad permissions simply to complete routine tasks.
The goal is to provide appropriate access without creating unnecessary friction.
Match Permissions to Real Responsibilities
Security teams should work with department managers and system owners to understand how resources are actually used. Permissions can then be designed around legitimate business requirements.
A useful access policy should answer three basic questions:
- Who needs access?
- What does that person need to do?
- How long should that access remain active?
Answering these questions can help organizations avoid both excessive permissions and unnecessary restrictions.
Conclusion
Effective access control requires more than passwords or a single security product. It is an ongoing process involving identity verification, authorization, permissions, physical security, monitoring, policy reviews, and timely removal of access.
The most common challenges include excessive permissions, complex policies, remote access, privileged accounts, inconsistent onboarding and offboarding, and outdated rules. Addressing these issues requires organizations to regularly review who has access, why they have it, and whether that access is still appropriate.
A practical access control strategy should support legitimate business activities while limiting unnecessary exposure. By combining clear policies with appropriate technology, monitoring, and regular reviews, organizations can build a more consistent approach to protecting systems, information, and physical resources.
FAQs
1. What is access control in cybersecurity?
Access control in cybersecurity is the process of determining who or what can access a system, resource, application, or data and what actions they are permitted to perform. It combines authentication, authorization, permissions, policies, and monitoring to limit access to approved users and activities.
2. What is the principle of least privilege?
The principle of least privilege means giving users, applications, or systems only the permissions they need to perform their required tasks. Limiting unnecessary privileges can reduce the potential impact of compromised accounts, accidental changes, and unauthorized activity.
3. How often should access permissions be reviewed?
Access permissions should be reviewed regularly and whenever an employee changes roles, leaves the organization, or receives temporary responsibilities. Organizations should also conduct periodic reviews of privileged accounts, inactive users, group memberships, and permissions for sensitive systems.