Field teams create IT problems that office-based policies rarely anticipate
An IT policy written for employees sitting behind desks assumes a lot. The device is usually on a known network. Power is available. The employee can walk over to somebody for help. Printers, monitors, docks, and replacement hardware are nearby. The workday happens in a controlled environment.
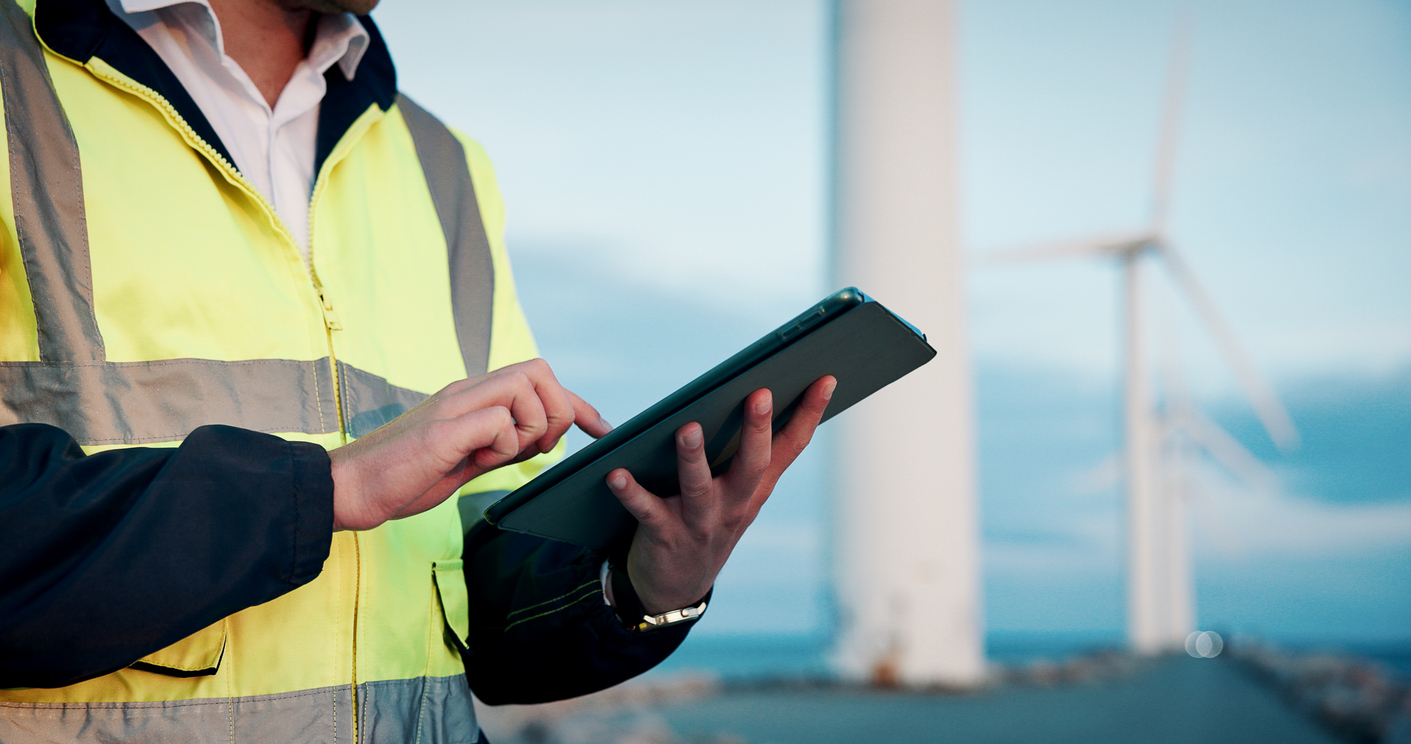
Field employees operate under different conditions. They may work from customer sites, warehouses, vehicles, temporary offices, construction locations, or industrial facilities. They connect through mobile hotspots and guest Wi-Fi, carry devices through weather and physical hazards, and sometimes need access to company systems when connectivity is poor.
If policies ignore those realities, employees usually invent workarounds.
Connectivity changes how people handle data
An office application that assumes a stable connection can behave very differently on a jobsite. Employees may download documents locally before leaving, take photos on personal phones, email files to themselves, or use consumer messaging apps because the approved system is slow over a weak connection.
Those behaviors often solve an immediate operational problem. They can also scatter company information across unmanaged devices and services.
Field-friendly technology planning starts by identifying what employees need to do when connectivity is good, poor, or completely unavailable. Some workflows need offline capability. Others may require a secure mobile connection or a different application design.
Mobile devices need an ownership model
Field work frequently blurs the line between company-owned and personal technology. A company may issue laptops but expect employees to use their own phones for authentication, photos, maps, or customer communication.
That arrangement can work, but the policy should say what the company is allowed to manage, which data may be stored on personal devices, what happens if a phone is lost, and how access is removed when the employee leaves.
NIST's guidelines for managing mobile devices in the enterprise cover both organization-provided and personally owned devices, including centralized device management and endpoint-protection considerations. Those questions become much more practical when employees spend most of the day away from the corporate network.
Support needs to account for distance
Office support processes often assume the device can be physically inspected. That is not always realistic when an employee is forty miles away, working a night shift, or at a customer location with a deadline.
Remote support tools, spare-device planning, standard hardware, and clear escalation procedures matter more for distributed teams. So does documentation. If a field employee loses access to a business application, the support team should know whether that blocks one person or an entire crew.
A company using managed IT services in Tacoma may have office staff, field employees, warehouses, and industrial locations across the same organization. The support model should reflect those different working conditions rather than treating every user as if they sit on the same network.
Field work creates more device lifecycle problems
Equipment that travels is more likely to be lost, damaged, replaced quickly, or transferred between employees. A laptop may move from one technician to another without returning to the office. Tablets may be shared across shifts. Phones can contain company photos and messages even when they are personally owned.
This makes inventory and retirement procedures important. The business should know who has each company device, whether encryption is enabled, how quickly a lost device can be locked or wiped, and what happens to data before equipment is reused or disposed of.
Remote access policy should match the actual environment
A blanket rule such as “never use public Wi-Fi” may be unrealistic for employees who spend every day on the road. A useful policy explains the approved alternative and gives employees technology that makes compliance practical.
NIST's enterprise telework and remote-access guidance recommends securing remote-access technologies and the client devices that use them. For field teams, that can translate into managed devices, strong authentication, encrypted connections, updated software, and clear rules for handling sensitive information outside the office.
Policies should be tested against a real day in the field
The easiest way to find gaps is to walk through common scenarios with the people doing the work.
What happens when a tablet breaks halfway through a shift? How does a technician retrieve a drawing at a site with weak cellular service? Can an employee report a lost phone after hours? Where should photos containing customer information be stored? How does a supervisor provision access for a temporary worker?
If the answer is “we usually just…,” there is probably an undocumented process worth fixing.
That review should include supervisors as well as IT. Field managers know which delays stop work, which locations have unreliable connectivity, and which unofficial workarounds employees rely on. Their input keeps policy grounded in operations.
Field teams do not need looser security or special treatment. They need technology rules designed around the environment they actually work in. Policies become much easier to follow when the approved process is also the fastest practical way to get the job done.