Penetration Testing vs Vulnerability Scanning: What Should a Growing Business Pay For First?
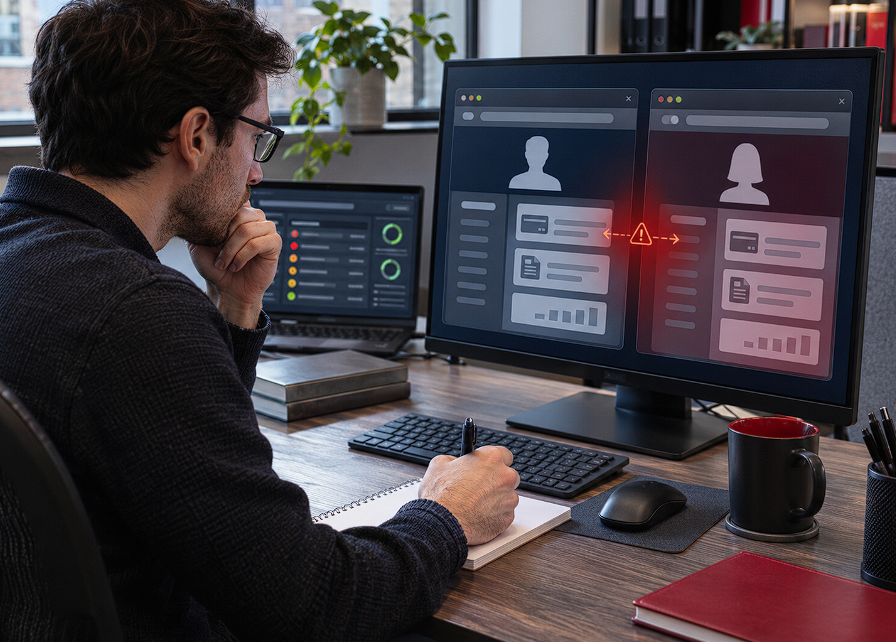
Vulnerability scanning finds potential security weaknesses in your IT systems, while penetration testing investigates whether those weaknesses can be exploited.
Both help businesses assess security risks, but they differ in depth, cost, and the evidence they provide.
For a growing business, the choice can affect its next contract: regular scans may still leave you without the penetration test report a major customer requires.
Why Growing Businesses Get Asked for Security Testing
Customers, insurers, and investors request security testing to assess the risks of working with your business.
A tender may require an independent report on your customer portal, while an insurer may ask how you find and fix weaknesses. Investors may request recent assessment results during due diligence.
These requests do not call for the same test. A scan of office laptops will not satisfy a contract requiring a test of your customer portal. Check the required system, test date, and report format before approaching providers.
Vulnerability Scanning: What You Get and What It Costs
Vulnerability scanning uses automated checks to flag potential security weaknesses, making it a lower-cost option for businesses needing regular checks. Many businesses get it through vulnerability management services, which combine recurring scans with prioritisation and progress tracking.
Each system or device checked is an asset, such as a website, server, or staff laptop. Finding a weakness is only the beginning:
- Run the scans: Automated tools check selected assets for known issues at an agreed frequency. Regular scans help find problems between deeper tests.
- Review the findings: Reports can contain false alarms or miss weaknesses. A vulnerability assessment can include reviewing results to decide what to fix first.
- Fix and verify: Your IT team or provider must address confirmed weaknesses and check whether the fixes worked. A scan report alone does not mean the issues are resolved.
When comparing providers, ask whether they also fix issues or leave that work to your IT team.
Providers may charge per asset or through monthly or annual coverage tiers. Costs depend on asset numbers, scan frequency, and human review.
Also, when comparing quotes, check whether setup, report reviews, and follow-up checks are included.
Penetration Testing: What You Get and What It Costs
Penetration testing investigates whether weaknesses can be exploited in an agreed system, making it worth prioritising when a customer requires a penetration test report or a sensitive application needs deeper scrutiny.
For instance, a tester might check whether one customer portal account can access another customer's information.
The scope determines how far that investigation goes. When comparing penetration testing services, check that the quote covers:
- Testing scope: Which websites, applications, networks, or cloud systems are included? Specify the account types and connected systems testers can examine.
- Testing work: What automated and manual checks will the specialist perform? Confirm exclusions before work begins.
- Test report: It should state what was tested and when, explain weaknesses and recommend fixes. Ask whether a customer will accept an executive summary.
- Retesting: Check whether the provider verifies fixes and supplies updated evidence. A retest generally covers agreed findings, not the whole test again.
Pricing generally reflects consultant day rates and testing days. A portal with several account types and connected systems may take longer than a simple website.
Ask providers to price initial testing and retesting separately. Budget for fixes, which are usually separate work.
For reference, the UK's National Cyber Security Centre recommends penetration testing alongside routine checks to gain assurance about vulnerability management.
A test assesses only the agreed systems at the time of testing; it cannot guarantee lasting security.
Side by Side: Which One Answers Which Question?
Use vulnerability scanning to track known weaknesses and penetration testing to investigate possible unauthorised access, choosing evidence based on what the customer or insurer requires.
Here is how each type of evidence matches common business requests.
So Which Should You Buy First?
Pay for regular vulnerability scanning first to catch known weaknesses, but prioritise penetration testing if a customer specifically requires it or a major release needs deeper checks.
Before committing your budget, consider four factors:
- Customer or insurer requirements: A request for an independent penetration test cannot be met by routine scan results. Confirm the systems, report age and acceptable evidence.
- Existing test reports: If you have a report, check its date, scope, and the tester's independence. Ask whether the customer also needs evidence of fixes.
- Upcoming system changes: A new customer portal or revised account permissions may warrant testing before launch, particularly when sensitive data is involved.
- Ongoing security needs: Without an immediate reason for a deeper test, scan regularly. Assign someone to review findings and verify fixes.
Take into consideration, in the UK government’s 2025 survey, 45% of large businesses said they had formally reviewed cyber risks posed by their immediate suppliers.
Those were supplier risk reviews, not necessarily requests for penetration testing, so the wording of your customer’s request still matters.
If you need a test, send providers the customer requirements and system details. Allow time for testing, reporting, fixes, and any retest.
A scan beforehand may help resolve known issues but should not delay the required test.
If the deadline is too tight, ask whether the customer will accept an extension or interim evidence.
How to Choose a Testing Provider
Choose a testing provider by comparing scope and deliverables, because a cheaper quote may exclude checks or evidence your business needs.
Give each provider the same brief and deadline. When reviewing proposals, check:
- Scope and method: Confirm included systems and user accounts. For scanning, check frequency and asset limits; for penetration testing, ask how much manual investigation is included.
- Qualifications and independence: Ask about testers' relevant experience and credentials, such as OSCP or CREST certifications. Confirm any independence requirements with the customer.
- Reports and dates: Request sample reports and confirm when the final report will arrive.
- Fixes and retesting: Agree who fixes weaknesses, whether a retest is included and what evidence follows.
- Pricing and data handling: Compare consultant days, asset limits, and extra fees. For overseas testing, check how your information will be accessed and handled.
Ask providers to confirm exclusions and additional charges in writing. A quote excluding systems connected to your customer portal may be cheaper than one covering the full application, even if both say penetration testing”.